 Photograph: Google (press image)
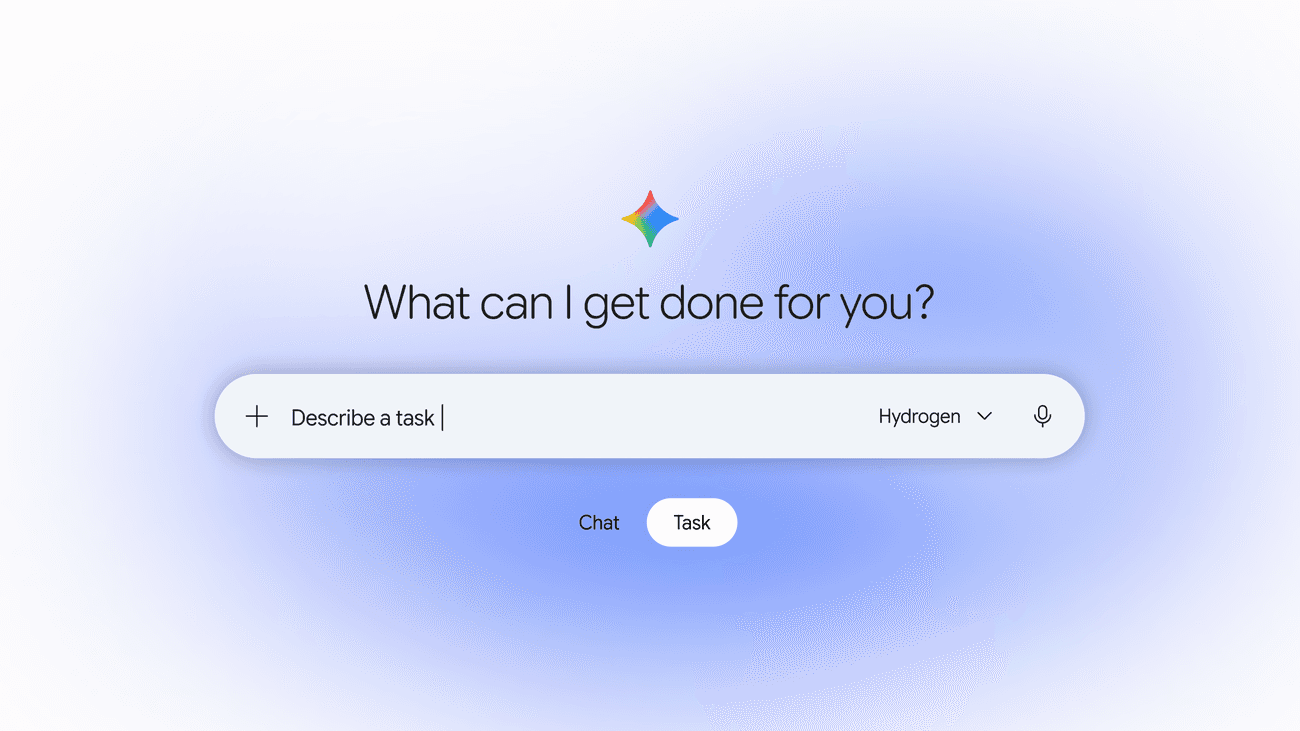
Google makes Gemini Tasks free in six countries
The rebranded Spark agent runs on Gemini 4 Hydrogen, with calls, payments and messaging available only in the US.
Jules Park, Nov 17, 2026
A security researcher found malicious JavaScript on 178 major sites served through Optimizely that tried to replace crypto addresses, skim cards and infect iPhones; recent iOS is patched.
Security researcher Scott Helme reported on Monday that malicious JavaScript was delivered through Optimizely, a website optimization platform, to visitors of 178 major websites in what appeared to be an attempt to steal cryptocurrency from iPhone users. The list of affected sites spanned major media outlets, banks, retailers and technology firms. According to 9to5Mac, the affected sites included BBC, CNN, HSBC, IKEA and Zoom. CNA reported that Salesforce and Equifax were also among the 178 organizations.
Helme said the rogue scripts tried to replace cryptocurrency addresses with the attacker's wallet, capture card numbers as they were entered, take cookies and screenshots, and run exploit code targeting iOS devices, according to CNA. Cybersecurity firm HudsonRock said it also saw signs that the affected sites had delivered malicious code to visitors, CNA reported.
Optimizely confirmed the incident, CNA reported. The company told CNA that it had identified unauthorized activity in which a vulnerability in its Experimentation tool was used to add malicious JavaScript to certain customer projects. Optimizely said it repaired the flaw, removed the injected code, and added safeguards to stop delivery of unauthorized code; it also said it had 'taken steps to secure' affected accounts, according to CNA.
Helme said nearly all of the rogue code had been removed, and Apple had released an iOS patch after a similar attack method was detected last month, 9to5Mac reported. He wrote that internal comments in the malware suggest that iOS versions 18.7.3 and later, and 26.3 and later, are protected, according to 9to5Mac. Monitoring the attacker's wallets, Helme found only $7,040 stolen, though it was not possible to determine how many payment card numbers were obtained, 9to5Mac noted.
Salesforce said it was investigating unauthorized Optimizely script changes and had disabled the scripts as a precaution, CNA reported. Equifax said it stopped using the platform and saw no evidence of a breach, while HSBC said the unauthorized scripts were not active on its websites, according to CNA. IKEA said it was looking into whether its digital services and customers could be affected, Awani reported. Apple, Zoom and CNN had not responded to requests for comment at the time of reporting, and Reuters said it could not determine whether the code succeeded in every case or how far any compromises went, CNA noted.
The incident highlights the risks of relying on third-party website software; according to Chainalysis, a blockchain intelligence firm, over $22.3 billion has been stolen in cryptocurrency hacks since 2021, CNA reported.
 Photograph: Asoundd/Wikimedia Commons (CC BY-SA 4.0)
 Photograph: Rockstar Games (press image)
 Photograph: Nvidia (press image)Photograph: Nvidia (press image)Photograph: Nvidia (press image)Photograph: Google (press image)
The rebranded Spark agent runs on Gemini 4 Hydrogen, with calls, payments and messaging available only in the US.
Jules Park, Nov 17, 2026
 Photograph: Joe Ravi (Shutterstock iStock Dreamstime)/Wikimedia Commons (CC BY-SA 3.0)
Users report unexpected sign-outs and App Store failures, while Apple's System Status page still lists the services as available and no restoration timeline has been given.
Sasha Lind, Nov 17, 2026
 Photograph: Coolcaesar/Wikimedia Commons (CC BY 4.0)
The state's attorney general says OpenAI lost control of its AI agents more than 80 times in testing and seeks penalties after the Hugging Face breach.
Sasha Lind, Nov 16, 2026