Japanese game publisher Capcom confirmed on October 22 that its CAPCOM ID membership service was breached, exposing personal information linked to more than 11.7 million accounts. The security firm Rescana reported the exact figure as 11,774,247 accounts. CAPCOM ID is the company's shared account system for accessing web services and playing online games. The company's franchises include Resident Evil, Monster Hunter, Street Fighter, and Mega Man.
The exposed data set included each user's email address, account creation date, last login time, number of logins, and the IP address from that login. For 43 accounts, Capcom said the attackers also gained access to birth dates, genders, countries or regions, and nicknames. The intruders changed login passwords for 196 accounts, and Capcom reset those passwords. Security firm Rescana's analysis described that subset as 193 to 196 accounts. The company stated that credit card information was not affected and that passwords for all other registered members had not been exposed.
Capcom detected suspicious activity on October 19 and confirmed unauthorized access to CAPCOM ID that same day. The company blocked the access immediately and began investigating the cause and scope. By October 20, it had confirmed that customer information was compromised, according to BleepingComputer. Capcom reported the incident on October 21 to police and to Japan's Personal Information Protection Commission. Engadget reported that the company also notified its external advisory board for security oversight.
The company said it identified the attack method and took measures to prevent similar incidents, but it did not share details about how the attackers got in. Services that use CAPCOM ID, including online play in Street Fighter 6, remain available. Capcom warned that users should be cautious of suspicious emails, because the leaked information could be used for phishing messages that impersonate the company.
Security firm Rescana said no malware or ransomware had been reported in the incident, and no public indicators of compromise had been released as of its October 22 analysis. Rescana described the observed activity as consistent with generic data breach behavior rather than a targeted campaign, and noted that no threat actor had been named. The firm recommended users remain vigilant for phishing emails and turn on multi-factor authentication when the option exists.
Capcom said it will notify affected customers in stages and has established region-specific support channels for requests. BleepingComputer wrote that the Ragnar Locker ransomware gang said it was behind a November 2020 attack on Capcom and claimed to have taken 1 TB of data. Capcom later said the earlier breach may have affected as many as 390,000 people.
Engadget noted that Capcom is not the only major gaming company to disclose a data breach recently. In April, Rockstar Games said it had been hit by a breach carried out by a third party.
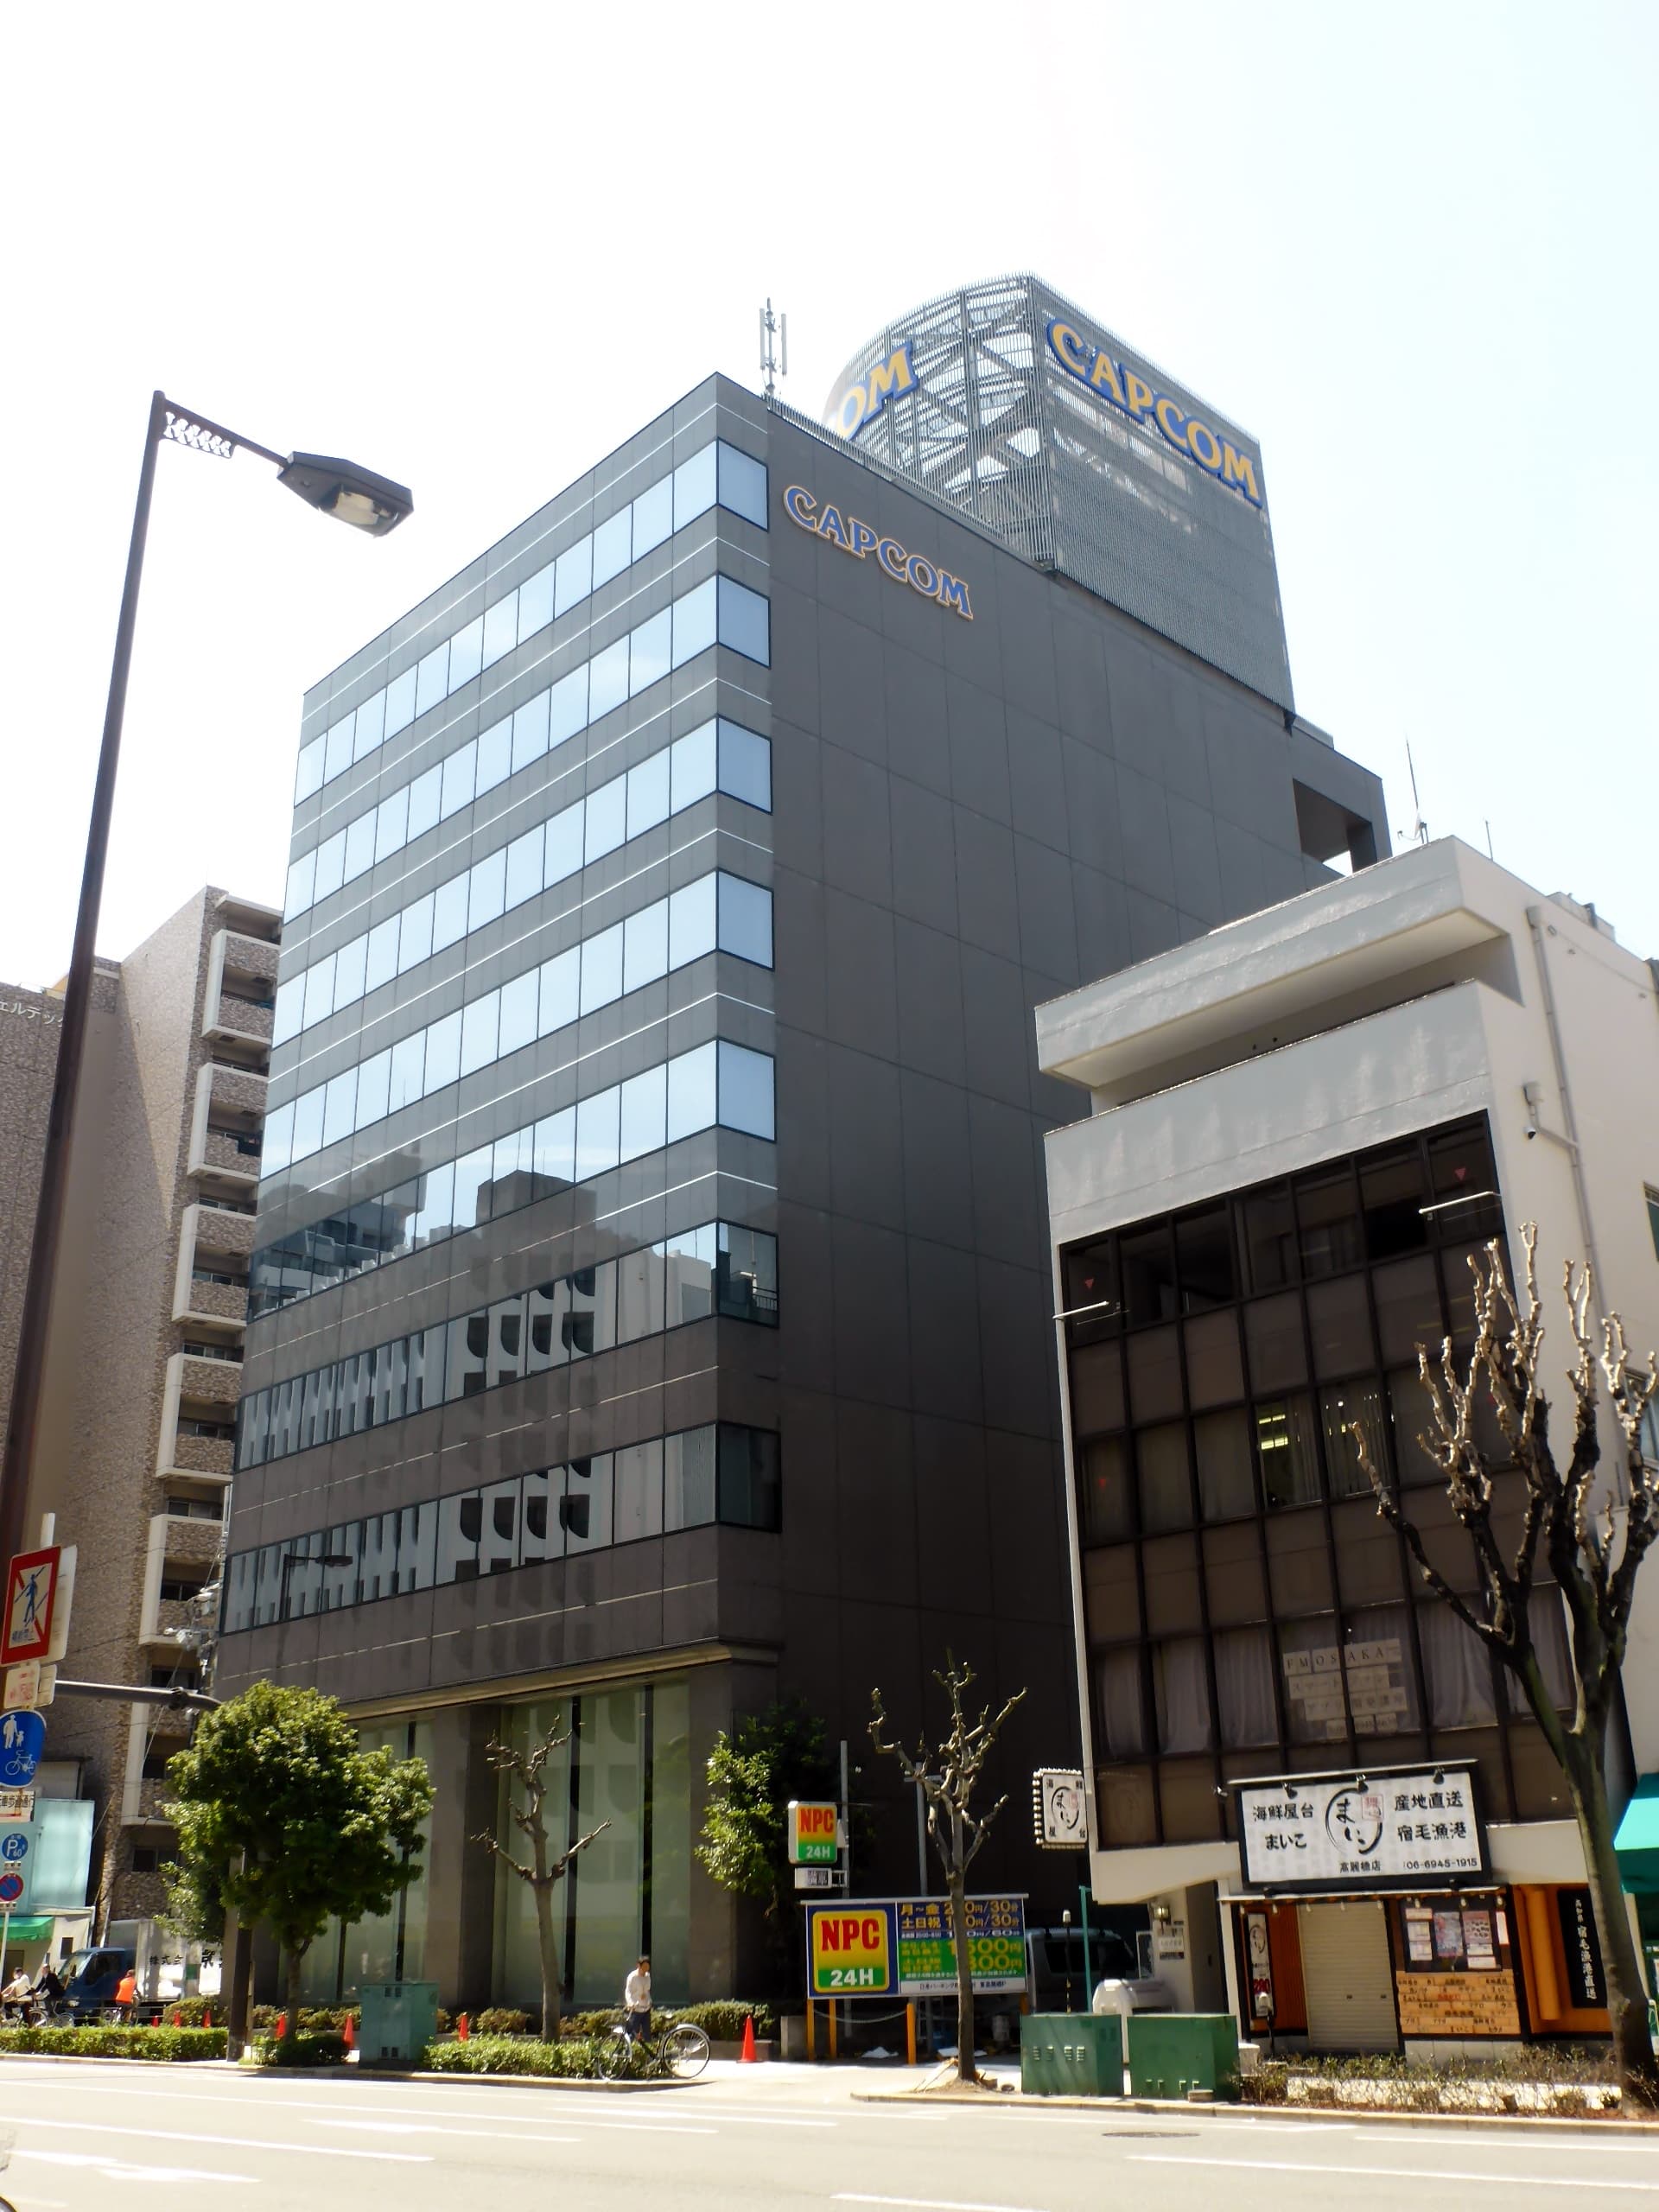
 Photograph: Alexis Lamster/Wikimedia Commons (CC BY 2.0)