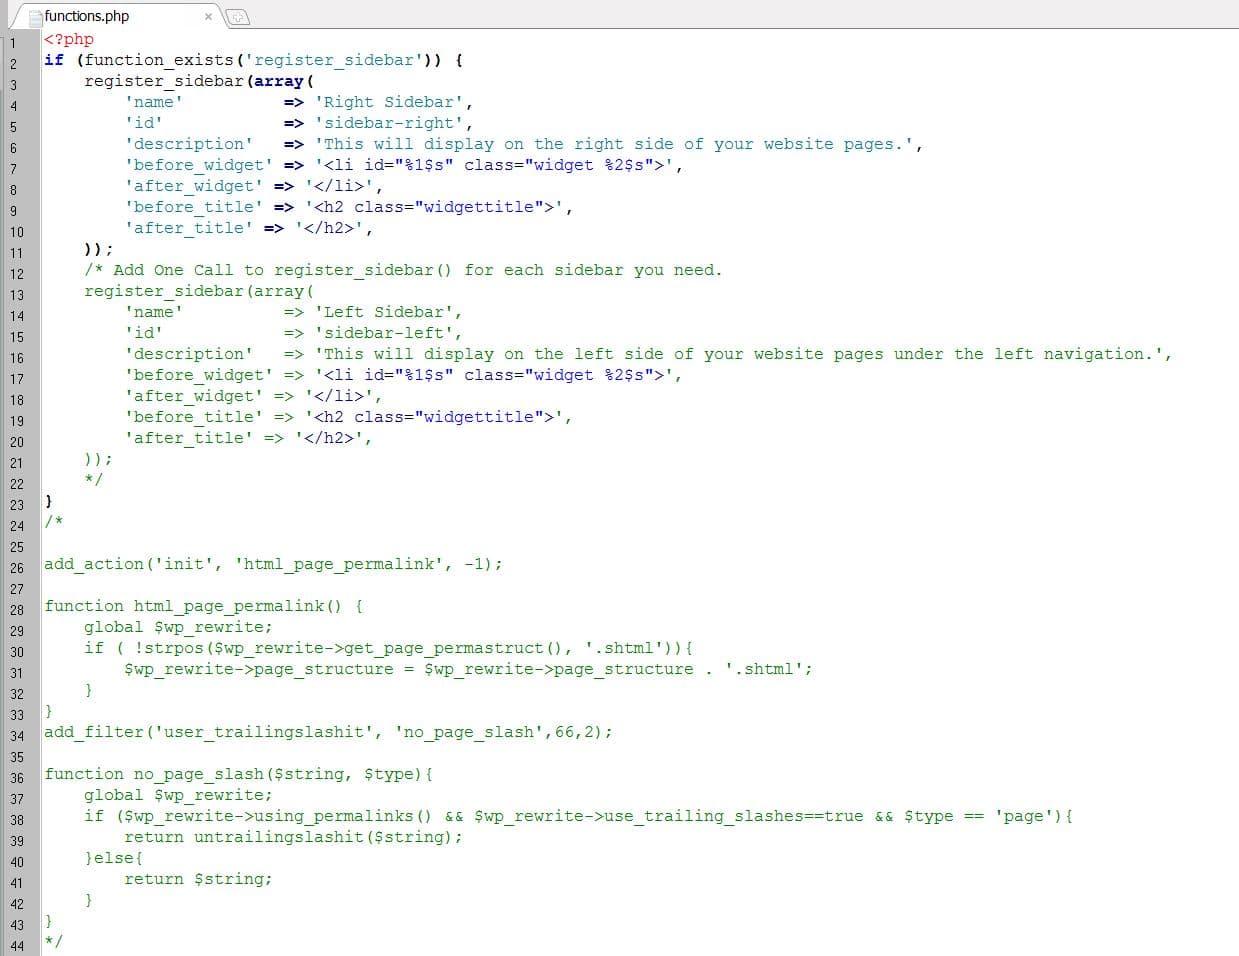
Two critical vulnerabilities in PHP, a programming language used across much of the web, forced government sites and popular services offline this week. The flaws, tracked as CVE-2026-109618 and CVE-2026-109619, can allow attackers to run their own code on affected servers, according to security firm watchTowr. PHP developers rate the vulnerabilities 9.2 out of 10 for severity. watchTowr says the remote code execution flaws affect every PHP version from PHP 5 onward, a span of roughly 20 years.
PHP underpins Wikipedia, WordPress, Drupal and many other platforms. By some accounts, up to 70 percent of websites use PHP in some capacity. Because many older PHP releases are no longer supported, sites that cannot apply the patch are at particular risk. Tiffany Farriss, interim CEO of the Drupal Association, told Reuters that all servers using any PHP version from the last 20 years will be vulnerable and that the issue impacts the majority of the internet.
As a precaution, some government websites in the Netherlands, Denmark, France and Finland were taken offline, Reuters reported. Canada's Minister of Artificial Intelligence and Digital Innovation, Evan Solomon, said the country temporarily took sites offline and urged operators using PHP to update as soon as possible. The NSA Cybersecurity account and the UK's National Cyber Security Center recommended taking systems offline if an immediate update is not feasible.
Several major sites went dark or restricted access. 4chan, DeviantArt and Wikipedia were affected, and Pokémon Home and Pokémon Champions were taken offline, according to Kotaku. The Internet Archive also went offline briefly before its operations team patched and restored service. Two long-running Japanese mobile games, World Quest and Save My Demonic World, are shutting down permanently because their developers say the games' older code cannot be patched, according to Kotaku.
Exploitation activity built quickly. Cloudflare CEO Matthew Prince said the company saw thousands of exploit attempts in the 10 hours before public disclosure, hundreds of thousands in the two hours after, and millions by the following night. Amazon Threat Intelligence reported an exploit attempt on October 17, days before the patch. OpenAI said a security researcher used GPT-5.6 Sol to identify the PHP flaws before attackers did, and it released a tool for developers to check for vulnerable PHP versions. Security firm Wiz called the flaws "among the most severe vulnerabilities discovered … in software history".
Update, October 24, 2026
Polygon reported on October 24 that Final Fantasy 14 was among the services hit by the PHP outage, though it did not go offline completely worldwide. Some players who could still access the game organized free "PHP Watering Service" posts on Reddit and X, offering to water other players' in-game gardens so their plants would not wither. Square Enix started allowing new logins after roughly 24 hours of work and had briefly paused the housing auto-demolition system; that system is set to resume on October 26, according to Polygon.
 Photograph: Coolcaesar/Wikimedia Commons (CC BY-SA 4.0)