Motorola launches Signature 27 with 7,000mAh battery and 200MP zoom
The $1,599 Android phone goes on sale November 26 with a 6.8-inch display, Snapdragon 8 Elite Extreme Gen 6, and seven years of OS upgrades.
Jules Park, Nov 7, 2026
A zero-click WAP Push message can drop calls, including emergency calls, and trap some phones in reboot loops; Google patched Android 14 through 17 in October.
A security researcher has disclosed an Android vulnerability called “SMS of Death” that lets a crafted WAP Push message crash the phone process handling calls without any user interaction, according to researcher Mark Blaszczyk. The flaw, tracked as CVE-2026-58882, can disconnect active calls, including emergency calls, and repeated messages can leave a device in a reboot loop. Google developed a fix on June 15 and included it in October security updates for Android 14 through 17, but the patch has not reached all supported devices.
Blaszczyk said a single malformed WAP Push message crashes com.android.phone, ending any active call, and requires zero interaction from the recipient. “The victim does nothing. No tap, no open, no notification,” the researcher said. The exploit sends an eight-byte payload; five of those bytes represent a header length. Android converts that value, 2,147,483,648, to a 32-bit integer without checking range, causing it to overflow to -2,147,483,648 and trigger a fatal error. The malicious message never appears in the user’s SMS inbox, according to the researcher.
Because the phone does not acknowledge receipt, carriers can resend the message, and it stays queued for retry on every boot. Blaszczyk said about 20 such messages can leave a device nearly unusable and may cause a bootloop. Android’s Rescue Party then forces the phone into recovery mode after about 90 seconds, which can lead the user to perform a factory reset. Recovery without wiping may require connecting the phone to a computer and deleting queued messages through Android Debug Bridge, according to Cybernews.
The researcher said he tested the exploit on a Pixel 9 with April 2026 firmware and several Samsung Galaxy A-series phones, achieving a 100 percent reproduction rate. The flawed code has existed since Android 12, and Cybernews says the vulnerability affects Android 12 through 16; Android Authority notes devices no longer receiving security patches may stay vulnerable.
Blaszczyk first reported the flaw to Google on May 5, but he said Google repeatedly dismissed it as a non-security issue; he publicly disclosed it on October 29. Android’s code records show the fix was added on June 15, and GrapheneOS later said Google distributed it through July security previews and it is slated for November’s Android Security Bulletin. Google included the fix in October security updates for Android 14 through 17, according to Blaszczyk and Cybernews, but rollout to devices from Samsung, Xiaomi, OnePlus, Motorola and others depends on each manufacturer. Users should check Software Update or System Update in Settings and install the latest available security patch.
 Photograph: Cristiano Tomás/Wikimedia (CC BY-SA 4.0)
 Photograph: Google (press image)
 Photograph: Alexis Lamster/Wikimedia Commons (CC BY 2.0)
 Photograph: Pokechu22/Wikimedia Commons (CC BY-SA 4.0)
 Photograph: The Conmunity - Pop Culture Geek from Los Angeles, CA, USA/Wikimedia Commons (CC BY 2.0)
The $1,599 Android phone goes on sale November 26 with a 6.8-inch display, Snapdragon 8 Elite Extreme Gen 6, and seven years of OS upgrades.
Jules Park, Nov 7, 2026
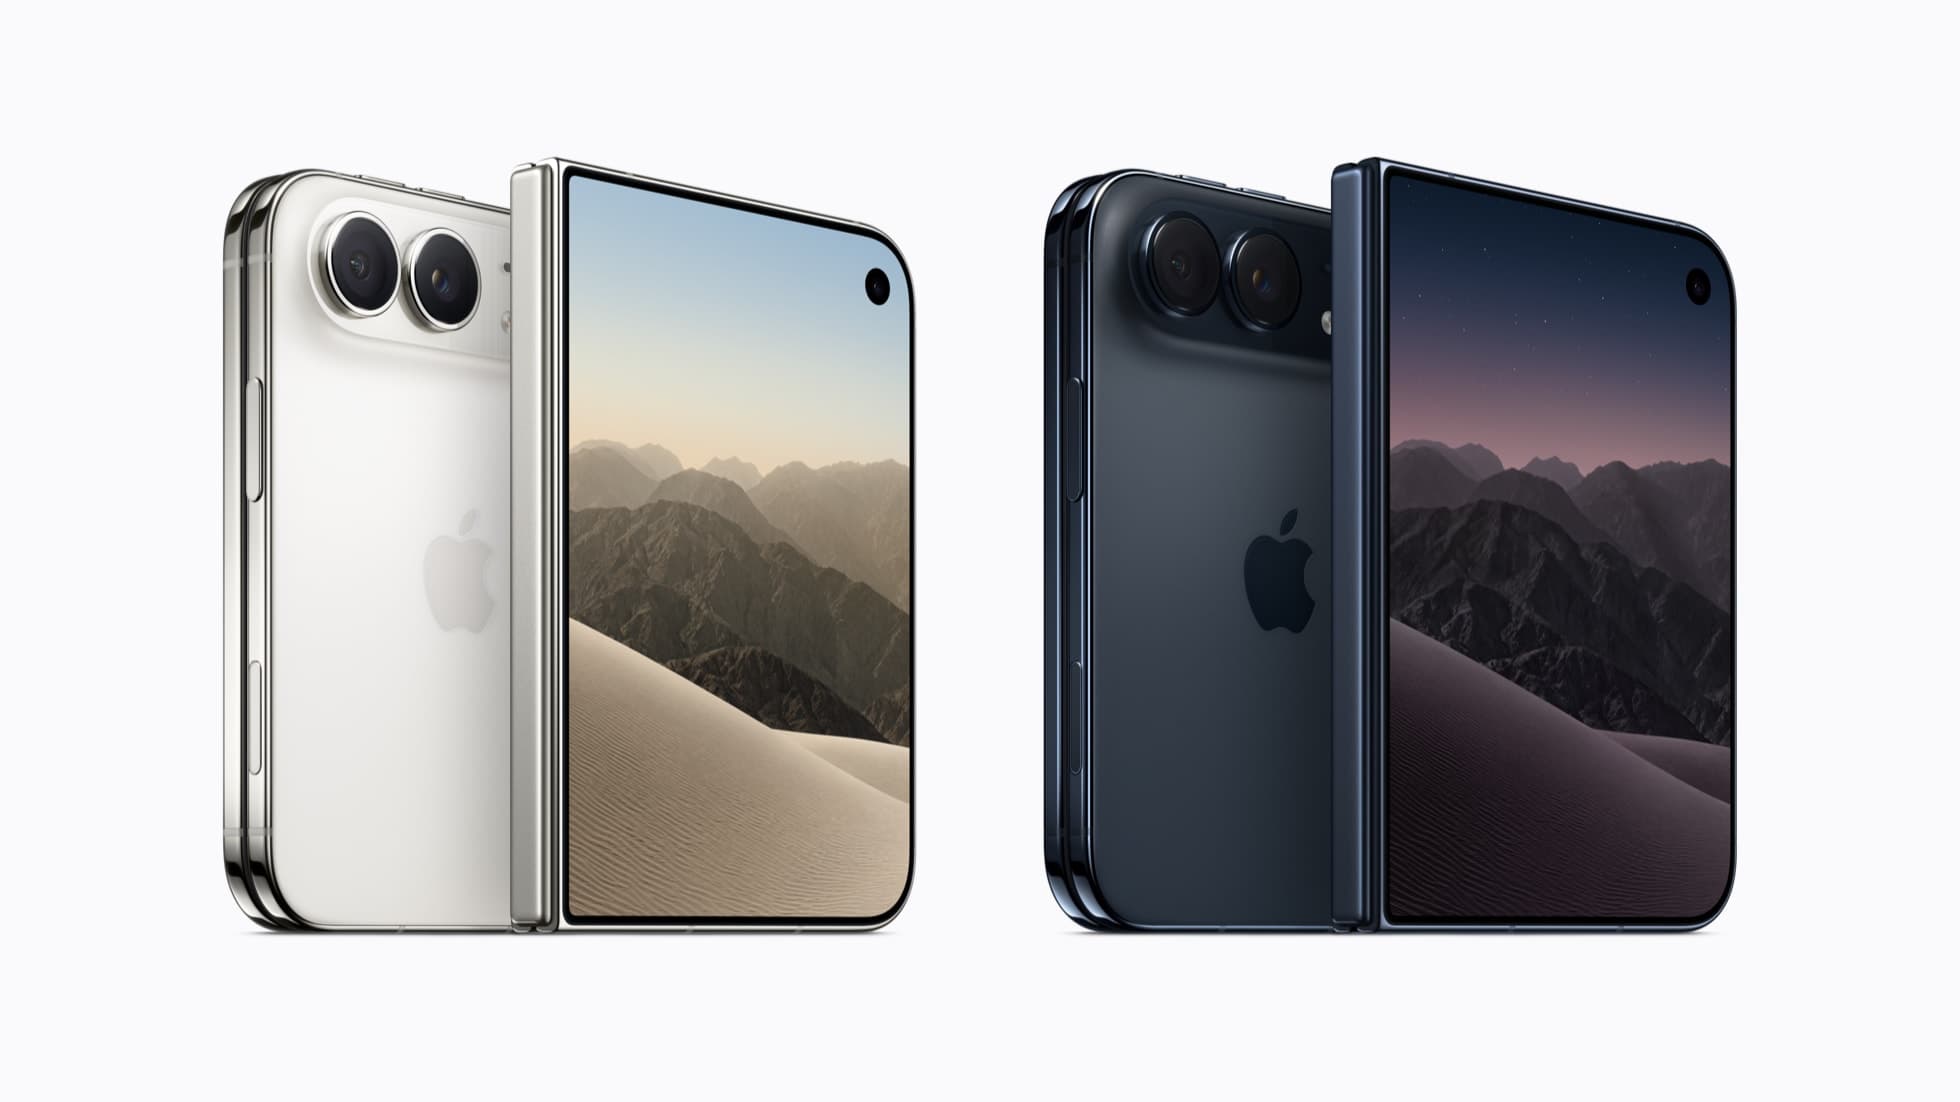 Photograph: Apple (press image)
Apple's first foldable starts at $1,999 and opened preorders on October 16. CNET's machine has folded it over 260,000 times, and Trend Micro warns about fake ordering sites.
Sasha Lind, Nov 5, 2026
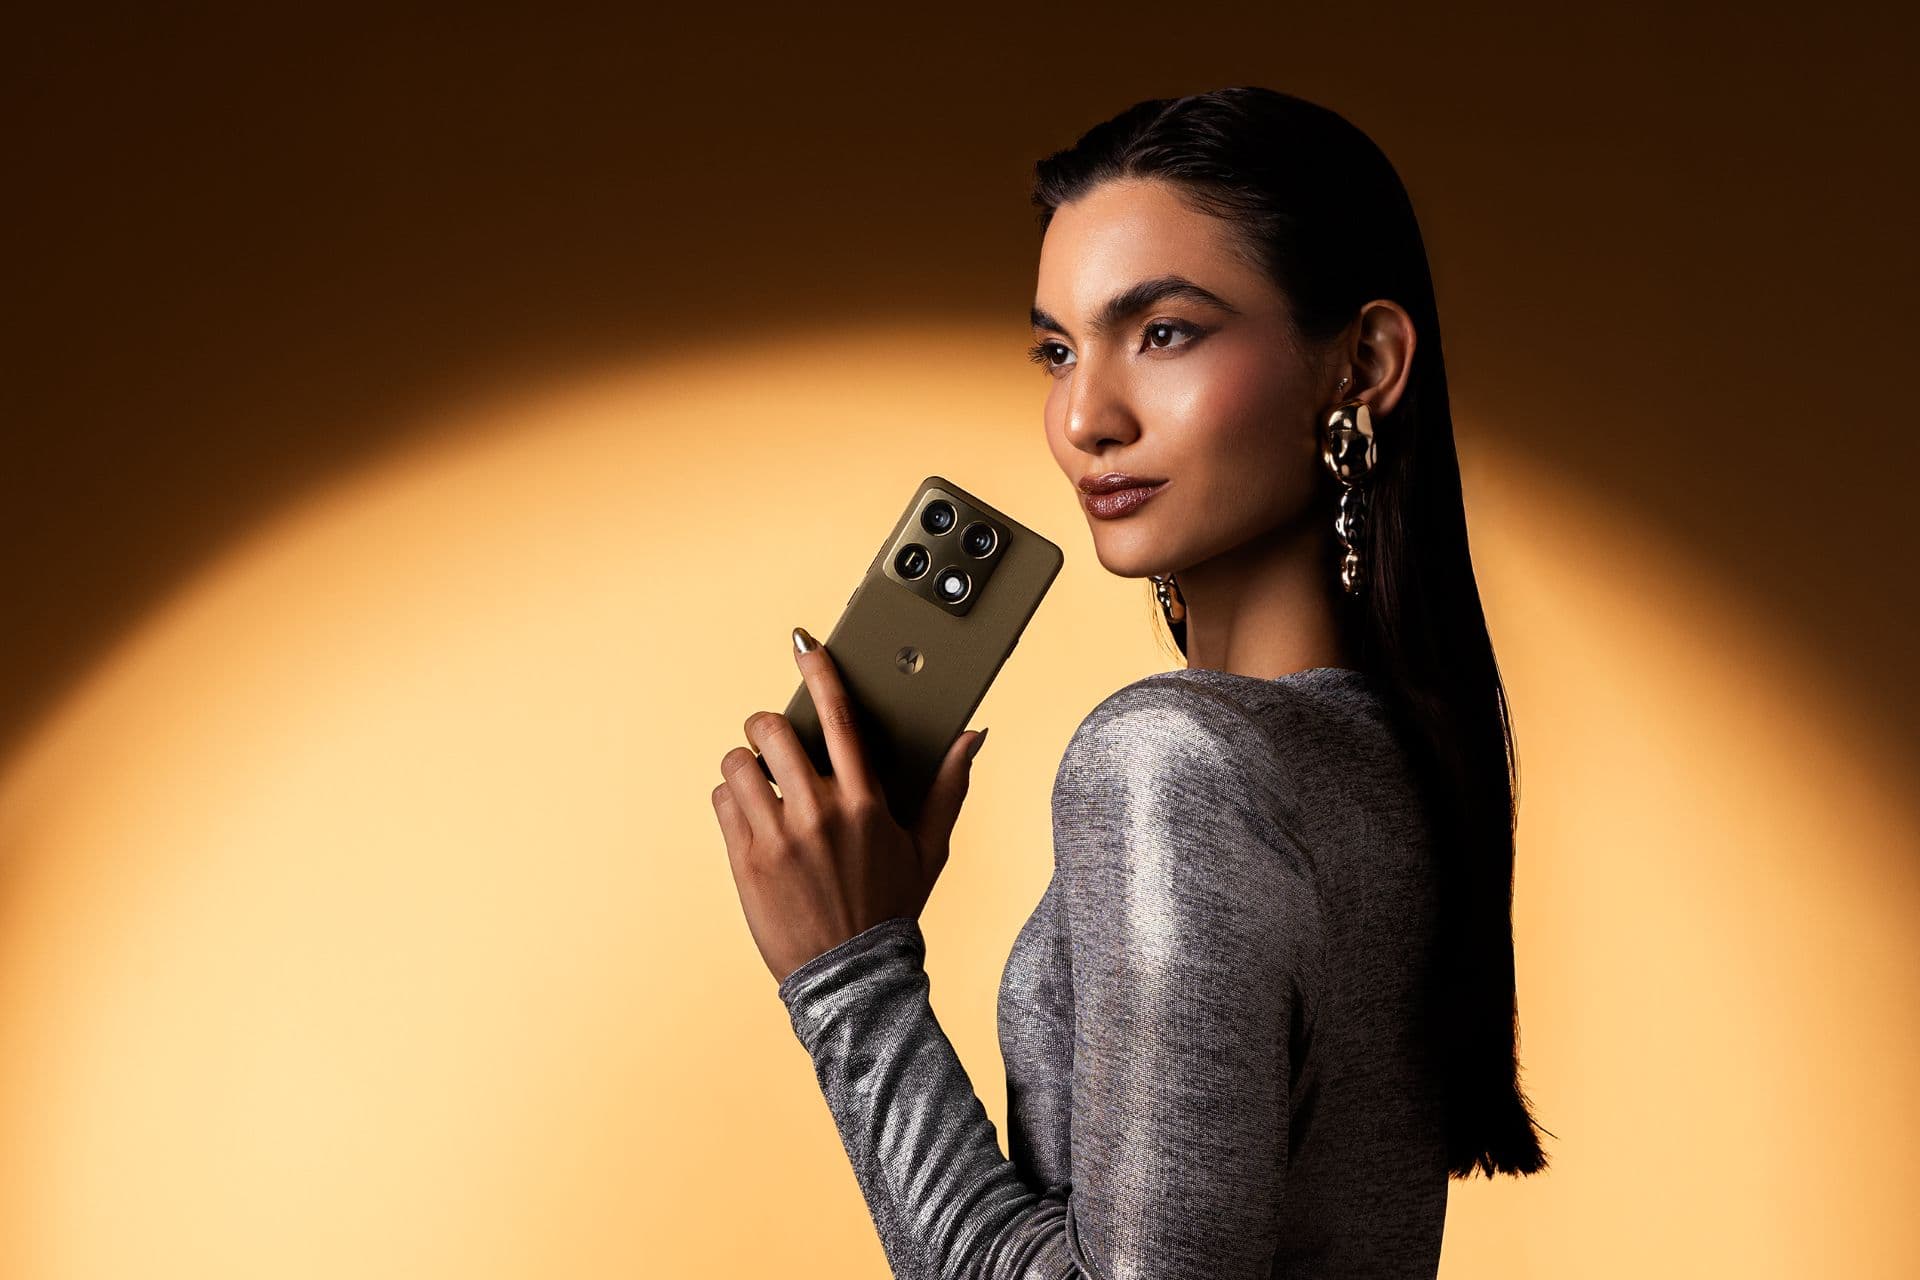 Photograph: Motorola (press image)
The 6.8-inch Android 17 phone packs a Snapdragon 8 Elite Extreme Gen 6, 7,000mAh battery and 200MP telephoto camera; pre-order dates differ by source.
Sasha Lind, Nov 5, 2026